Spectra is
SOC 2 Type II Certified
At Spectra, we take data security very seriously. Our print and distribution facility is SOC 2 Type II certified, giving our clients the assurance that when they trust us with their databases, address lists, and personal information about clients, members, patients, and customers, that information is protected according to current best practices.
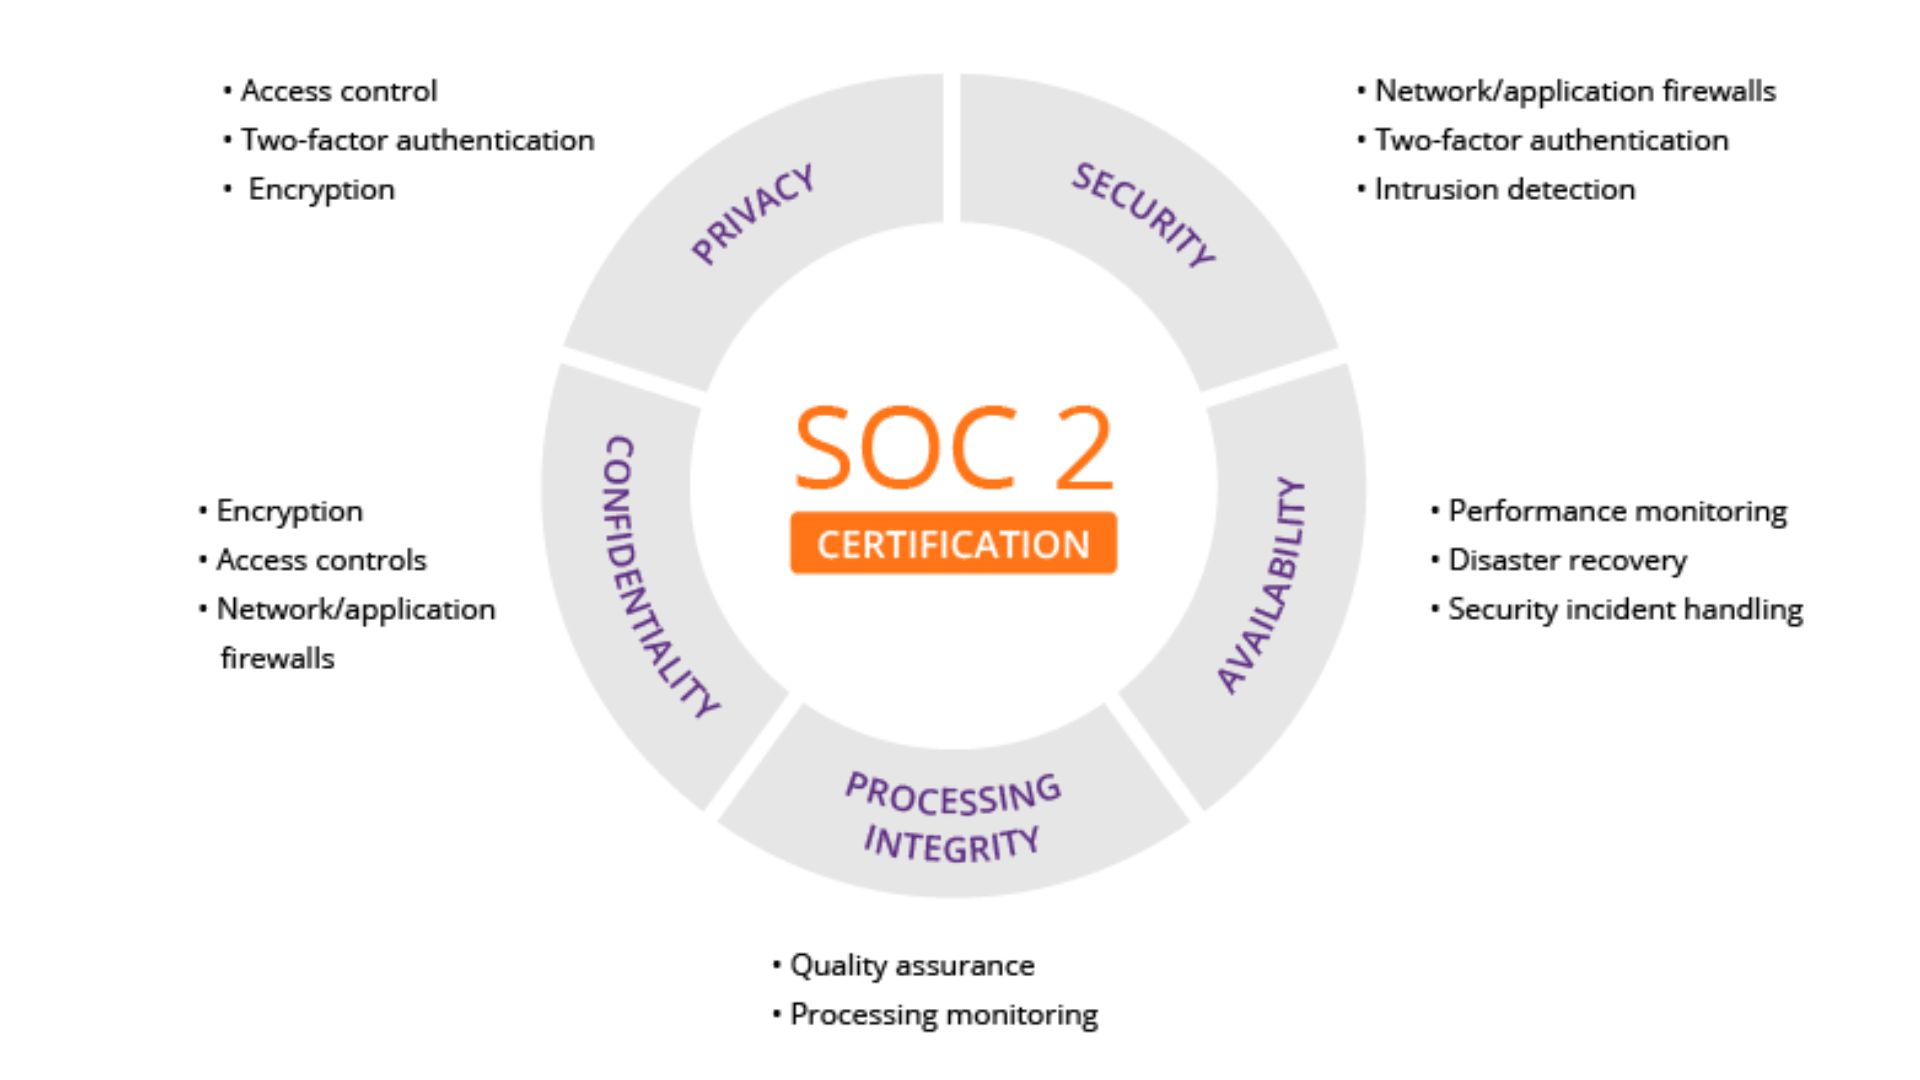
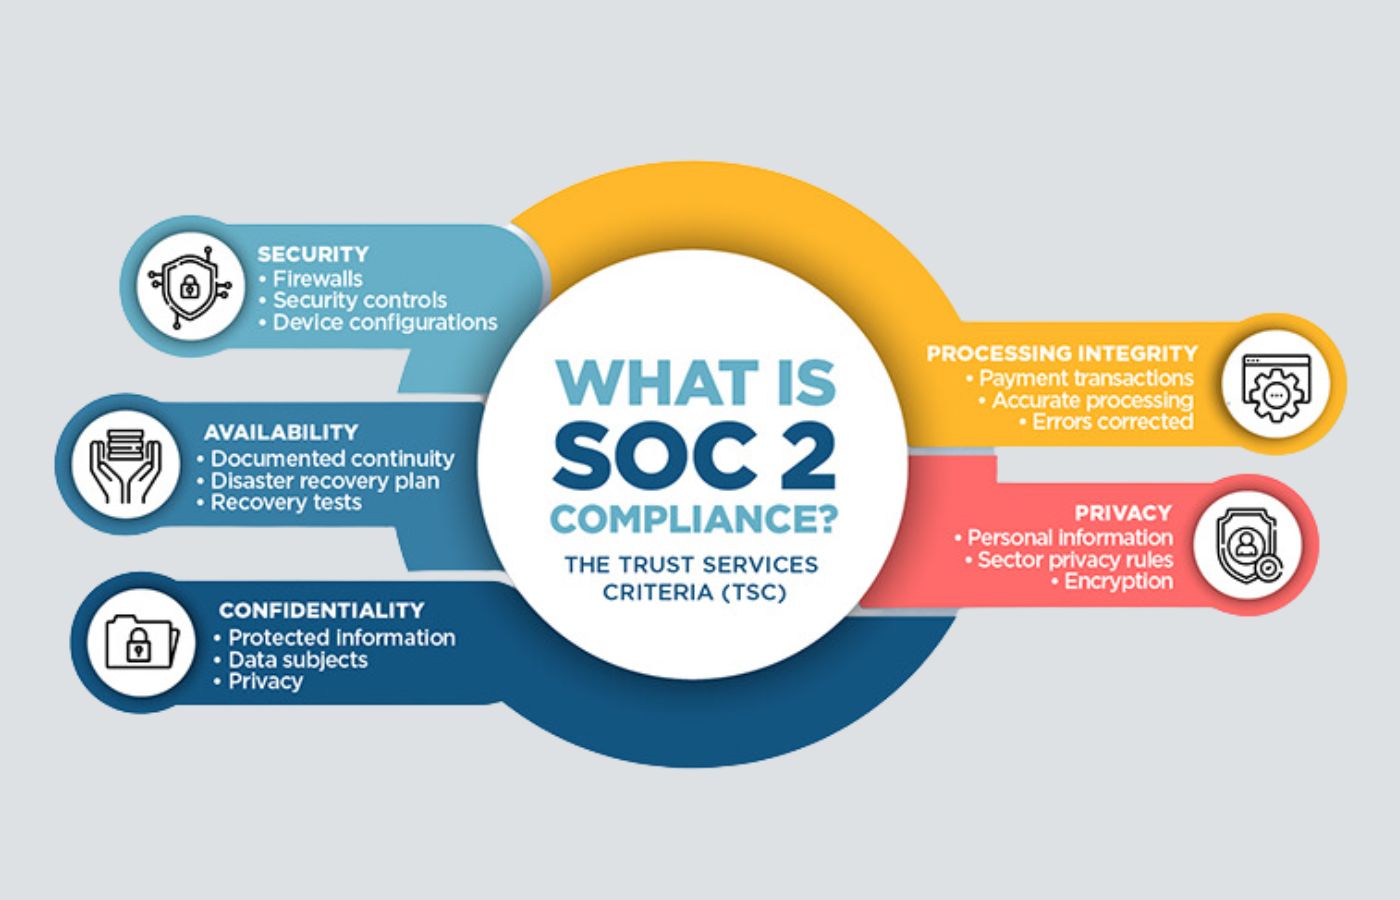
SOC 2 Type II Certification Explained
As a provider of SOC 2 compliance services, Spectra is an appropriate print and mail provider for clients that require verifiable data security practices. Government agencies, insurance providers, financial services, and healthcare organizations are just a few examples of clients that must be able to show that the service providers they use are certified in keeping protected information from being exposed during projects.
SOC 2 certification has two different types, based on the frequency of auditing. Type I certfication is based on a single “snapshot” of the organization’s data security practices. Type II certification is based on regular annual audits, giving clients greater assurance that the organization’s responsible data security practices are being followed on an ongoing basis. Spectra holds SOC 2 Type II certification, with independent auditors regularly checking our network security, employee practices, physical environment, and other elements of our organization for compliance.
Features of Spectra’s Data Security Practices
There are many different aspects of a successful approach to data security. Spectra maintains these and other best practices to protect the information we handle for clients while conducting their projects.
- Network security. Experts on our team ensure that our networks are protected by firewalls and software, updated with the latest patches to keep hackers from accessing information stored on our computers and servers.
- Secure transfer and data destruction protocols. We follow secure methods when obtaining address lists from clients and returning them after a project. While we have a database in our control for a project, we limit access within our team and keep it on our secure network. After a project is concluded, we return the information as soon as possible or delete/destroy it according to secure protocols.
- Employee training. Our team is regularly updated on best practices for handling data in a secure manner. We also ensure that our team avoids posting any information publicly that could enable hackers to obtain access to our network.
- Physical environment. Document management and destruction are conducted under strict protocols, and our physical environment is secured to prevent unauthorized members of the public from gaining access to protected data.
What SOC 2 Type II Certification Means for Spectra’s Clients
Why does it matter that Spectra is SOC 2 Type II certified? Many of the clients we work with are under obligation to keep the sensitive data of their patients or members secure at all times. When they share that data with a third party service provider to conduct a printing and mailing project, they must have assurances that the provider they choose is compliant with the same regulations that govern their handling of data.
Spectra’s SOC 2 Type II certification provides clients with that assurance, keeping them in compliance with federal and state regualtions. Our print and mail services are qualified for clients who need to send communications to individuals based on their financial account information, medical diagnosis, and other factors that are strictly regulated by law.
1. Assessment Scope
Define the scope of services and systems that will be assessed under SOC 2 compliance.
2. Gap Analysis
Conduct a gap analysis to identify areas where current practices may not meet SOC 2 requirements.
3. Policy and Procedure Development
Develop and implement policies and procedures to address security, availability, processing integrity, confidentiality, and privacy.
4. Security Controls Implementation
Implement appropriate security controls such as access controls, encryption, and monitoring systems.
5. Internal Audit
Conduct internal audits to assess the effectiveness of implemented controls and processes.
6. Remediation
Address any identified gaps or deficiencies through remediation activities.
7. SOC 2 Type I Report
Obtain a SOC 2 Type I report from an independent auditor confirming the design and implementation of controls.
8. SOC 2 Type II Report
After maintaining controls for a minimum period (typically 6-12 months), undergo a SOC 2 Type II compliant audit to validate the operational effectiveness of controls over time.
GET IN TOUCH WITH SPECTRA!
Contact us today and experience the difference of working with a partner dedicated to your success.
Frequently Asked Questions
HIPAA compliance is related to SOC 2 certification, but is not the same. Federal law encoded under HIPAA gives specific guidelines for the handling of patient health information (PHI). Spectra is also 100% HIPAA compliant in its print and mailing services.
Data breach notification letters are an important service that Spectra provides. If your organization has been hit by a cyber attack or accidental exposure of private information, Spectra can print and mail notification letters in a secure manner, with timely and affordable service.
Secure mail is a special area of expertise for Spectra. We provide pressure seal mailing services as a primary method for mailing confidential information to individuals. Blank cover letters, secure envelopes, and other options are available as well. Schedule a consultation with Spectra to learn about these and other secure mailing methods and select the one that best fits your organization’s needs.
Our Location
Get in touch with us today to find out more about how Spectra’s Fulfillment Service Center and Warehouse can help.